Question bank
RFP questions on data, security and compliance
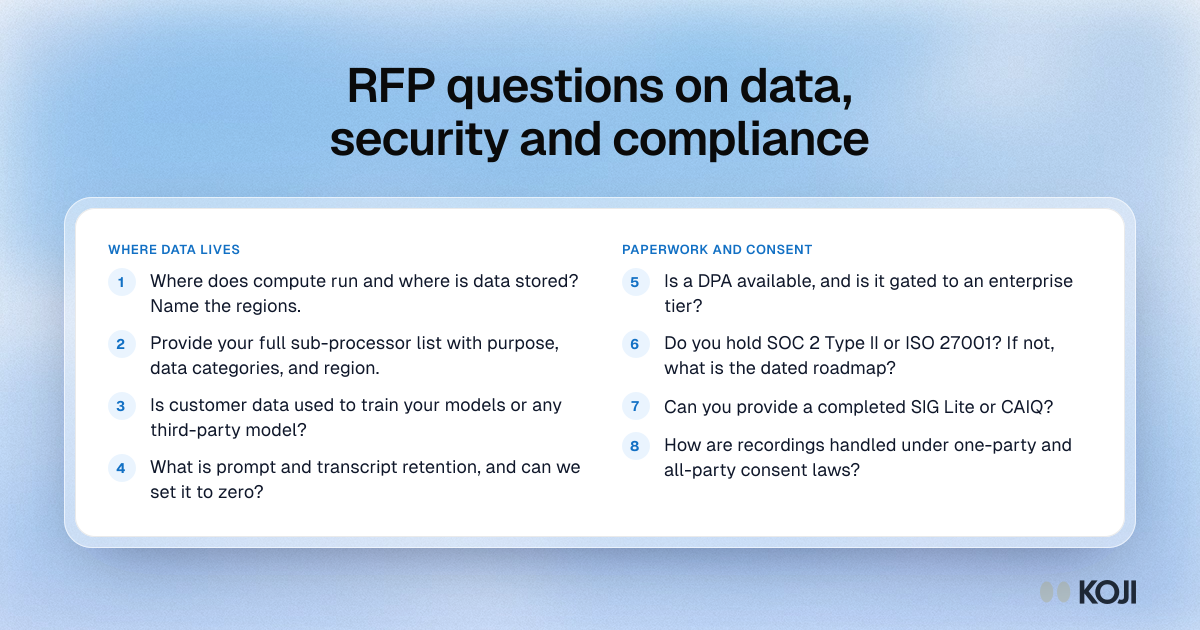
Eight data, security and compliance questions for user research platform vendors: where compute and data live, sub-processors, whether your data trains models, retention, DPA access, SOC 2 or ISO 27001, security questionnaires and recording consent. Asking them early avoids a security review that stalls the deal after the demo.
Where this appears
What's in this question bank
Where data lives
- Where does compute run and where is data stored? Name the regions.
- Provide your full sub-processor list with purpose, data categories, and region.
- Is customer data used to train your models or any third-party model?
- What is prompt and transcript retention, and can we set it to zero?
Paperwork and consent
- Is a DPA available, and is it gated to an enterprise tier?
- Do you hold SOC 2 Type II or ISO 27001? If not, what is the dated roadmap?
- Can you provide a completed SIG Lite or CAIQ?
- How are recordings handled under one-party and all-party consent laws?
Use this image
Free to use in your docs, decks and posts under CC BY 4.0, as long as you credit Koji with a link to this page. To embed it, paste this into your page:
html
<a href="https://www.koji.so/visuals/rfp-questions-research-data-security-compliance"><img src="https://www.koji.so/visuals/rfp-questions-research-data-security-compliance/rfp-questions-research-data-security-compliance.png" alt="Question bank of eight RFP questions on research platform security: data regions, sub-processors, model training, retention, DPA, SOC 2 and consent." width="1200" height="630" /></a>
<p>Source: <a href="https://www.koji.so/visuals/rfp-questions-research-data-security-compliance">RFP questions on data, security and compliance</a>, Koji</p>